AI is already inside your business.
Not because you approved it. Not because IT rolled it out. Not because anyone reviewed the terms.
It is there because someone on your team used ChatGPT to clean up an email. Someone pasted a spreadsheet into Claude to summarize it. Someone asked Copilot to draft a proposal. Someone used Gemini to rewrite client notes.
They were not trying to create risk.
They were trying to get work done.
That is exactly why this matters.
Shadow AI is the new shadow IT
For years, businesses worried about employees using unapproved apps, personal cloud storage, and unmanaged devices.
Now the same problem has moved into AI.
Shadow AI means employees are using AI tools outside company policy, outside IT oversight, and outside any clear security process.
Most business leaders do not know it is happening. Most employees do not understand the risk. They see a helpful tool, type in a prompt, paste in some information, and move on.
The problem is what they paste.
Client lists. Financial reports. HR records. Draft contracts. Internal strategy documents. Legal notes. Vendor pricing. Proposal language.
That information can move outside your company’s control in seconds.
The personal device problem makes this worse
A lot of businesses have done the right things on company systems.
They use endpoint protection. They enforce MFA. They manage updates. They control access. They restrict risky settings. They monitor for threats.
But employees also have personal laptops, home computers, tablets, and phones.
Those devices are not always managed. They are not always patched. They do not always have business-grade protection. They may already have browser extensions, AI apps, sync tools, file-sharing tools, or personal accounts connected.
Now picture this.
An employee installs an AI tool on a personal laptop. They connect it to a personal account. They use it to summarize a work file. Then they log into company email, the CRM, SharePoint, Google Drive, or another business system from that same device.
Your data is now touching a machine you do not control.
That is the part many AI conversations miss.
This is not only about what someone types into a chatbot. It is about where they use it, what device they use, what account they connect, and what company systems that device can reach afterward.
That is why AI governance cannot just be a software decision. It has to include policy, device rules, user training, data classification, access control, and approved tools.
The risk is not AI. The risk is unmanaged AI.
CasCom is not anti-AI.
Blocking AI outright is not realistic, and it is not smart. Businesses that learn how to use AI properly will move faster. They will reduce manual work. They will improve documentation, reporting, service delivery, and decision-making.
But unmanaged AI is a different story.
When an employee uses a free or personal consumer AI account, your business usually has no control over:
- Who owns the account.
- What data gets entered.
- Where that data is stored.
- Whether prompts are retained.
- Whether data can be used to improve the service.
- Whether access is tied to a personal email.
- Whether the tool connects to files, email, calendars, or apps.
- Whether the employee leaves and takes the AI history with them.
That is not a productivity strategy.
That is a data exposure problem.
AI tools are becoming more powerful
The first wave of AI tools felt simple. A blank chat box. A question. An answer.
That phase is ending.
Modern AI tools are moving toward agents, assistants, browser automation, file access, calendar access, email access, and workflow execution.
An AI tool that rewrites an email creates one level of risk.
An AI tool that can access company files, summarize inboxes, connect to systems, trigger workflows, or act on behalf of a user creates a much bigger governance issue.
That does not mean you avoid these tools.
It means you choose them deliberately.
Some platforms are built for managed, business-focused AI deployment, including MSP-led and multi-tenant environments. Hatz.ai is one example in that category. The point is not that every business needs the same platform. The point is that every business needs an intentional AI stack instead of a pile of employee-selected tools.
Do not let every department pick its own AI tool.
Pick the right tools, configure them properly, and make sure your people understand what belongs in them and what does not.
AI governance does not need to be complicated
A good AI policy does not need to be 40 pages long.
It needs to answer the questions your employees already have, even if they have not asked them out loud.
Can I use AI for work?
Which tools are approved?
Can I paste client information into AI?
Can I upload contracts, financials, or HR documents?
Can I connect AI to my email or calendar?
Can I use AI on a personal device?
Who approves a new AI tool?
What do I do if I already entered sensitive data into an AI tool?
What work still needs human review?
The goal is not to slow people down.
The goal is to remove guesswork.
Because when employees have no guidance, they make their own rules.
What a safe AI rollout should include
CasCom recommends every business put four controls in place before AI use spreads further.
1. Create an AI Acceptable Use Policy.
This is the baseline. It defines approved tools, banned use cases, sensitive data rules, review requirements, and who owns oversight.
2. Train the team.
Policy without training will fail. Employees need plain-language examples of what they can and cannot enter into AI tools. They need to understand why “summarize this client file” can create real exposure.
3. Approve AI platforms intentionally.
Do not let tool selection happen by accident. Choose platforms that fit your security, privacy, workflow, and operational needs.
4. Treat AI like part of your security program.
AI needs the same discipline as email, cloud storage, remote access, and endpoint protection. That means identity controls, access reviews, logging, vendor review, data handling rules, and incident response planning.
CasCom AI is about useful AI without reckless exposure
CasCom AI is built around a simple belief.
AI should help your business move faster without handing sensitive data to tools nobody reviewed.
That means we help clients:
- Create practical AI policies.
- Identify risky Shadow AI use.
- Choose approved AI tools.
- Secure AI access and workflows.
- Train employees on safe AI use.
- Review where business data is being entered, uploaded, or connected.
The real opportunity is not just using AI.
The opportunity is using AI in a way your leadership, clients, insurers, auditors, and employees can trust.
Start with the policy
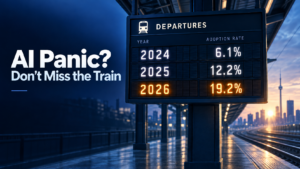
AI adoption is not slowing down.
Your employees will use it. Your competitors will use it. Your vendors will use it. Your clients will start asking how you use it.
The worst position is pretending it is not happening.
The better move is to put a simple policy in place, train your team, approve the right tools, and build from there.
That starts with a clear AI policy.
CasCom has created a general-use Corporate AI Policy template to help businesses set a baseline quickly. It is not the whole AI governance program. It is the first step.
Fill out the form and we will email you the PDF template.
Request your ready-to-use Corporate AI Policy: [insert url]